
Blog
Keep herdr, give each agent its own microVM
Brig now supports herdr. The herdr profile runs each coding agent in its own Brig microVM and lets one herdr client manage all of them over SSH, with no open port in the guest. A new herdr plugin, herdr-brig, turns the setup into one key: it boots a sandbox for a project, registers it as a herdr machine, and starts Claude Code in it. Another key removes it. This post covers what shipped, how to set it up, and its limitations.
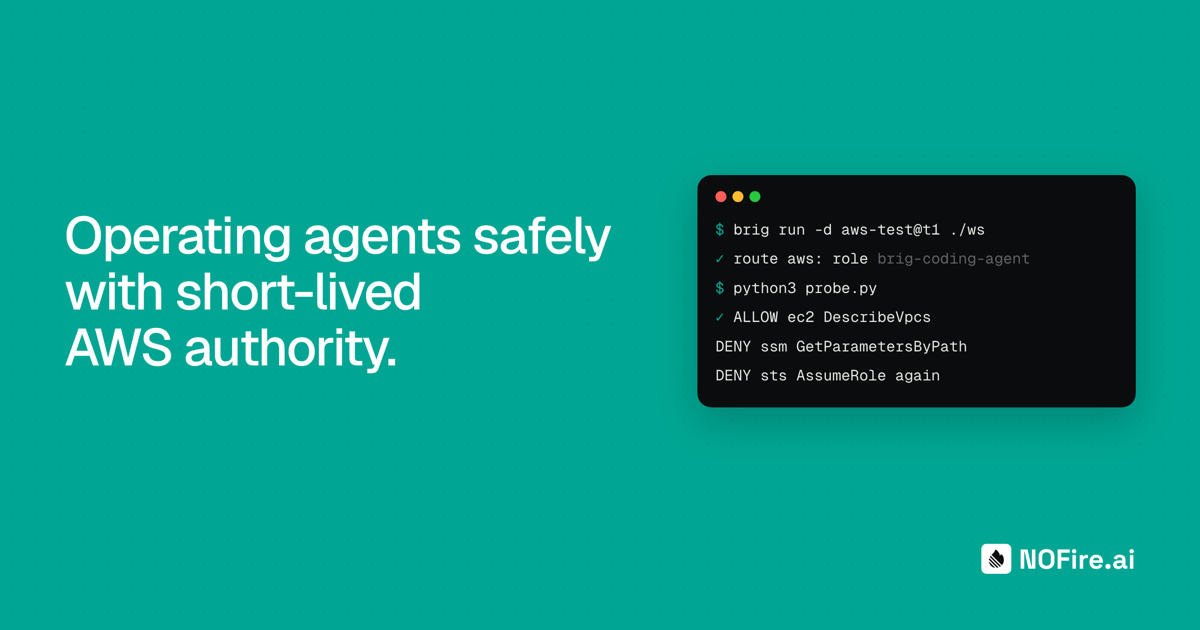
Operating agents safely with short-lived AWS authority
A coding agent that reads AWS will pick up your own SSO session if you let it, and CloudTrail cannot tell its calls from yours. This post builds the alternative with Brig v0.5.1: a dedicated IAM role with a narrow policy, 30-minute keys vended into a microVM by a broker on the host, and an audit trail that joins every AWS call to the sandbox that made it and the developer who started it.
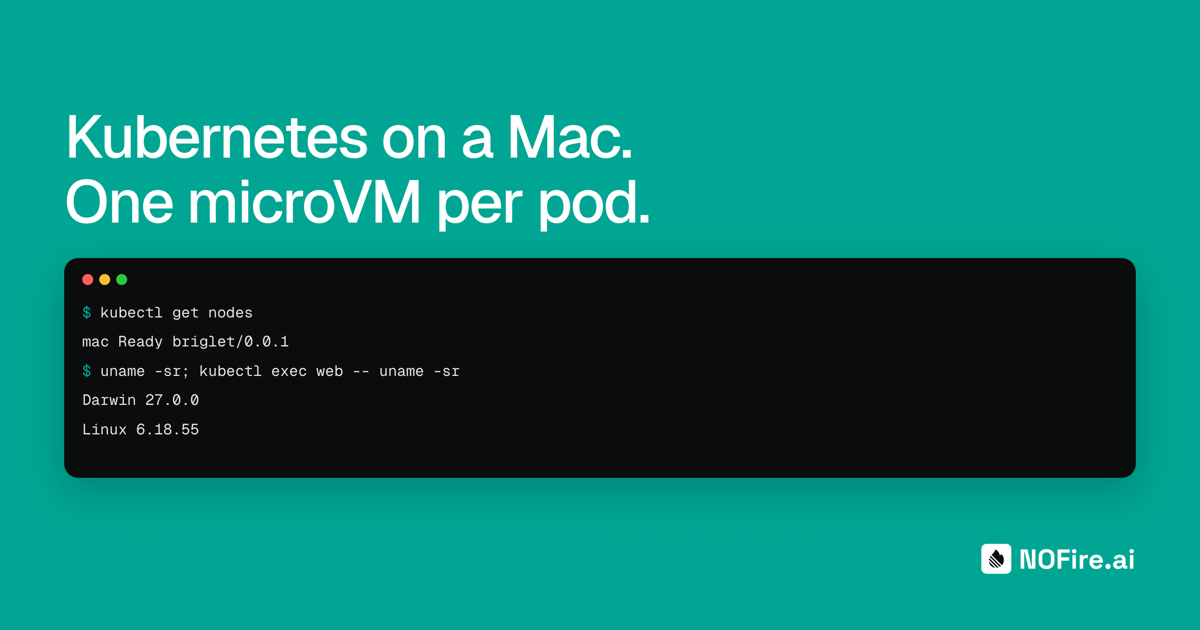
Kubernetes on a Mac, one microVM per pod
Briglet runs the Kubernetes control plane and a node agent as macOS processes on Apple silicon, and boots every pod as its own Linux microVM. This post installs it on a clean Mac, follows a pod into its VM, routes a Service without kube-proxy, and reads the conformance results.
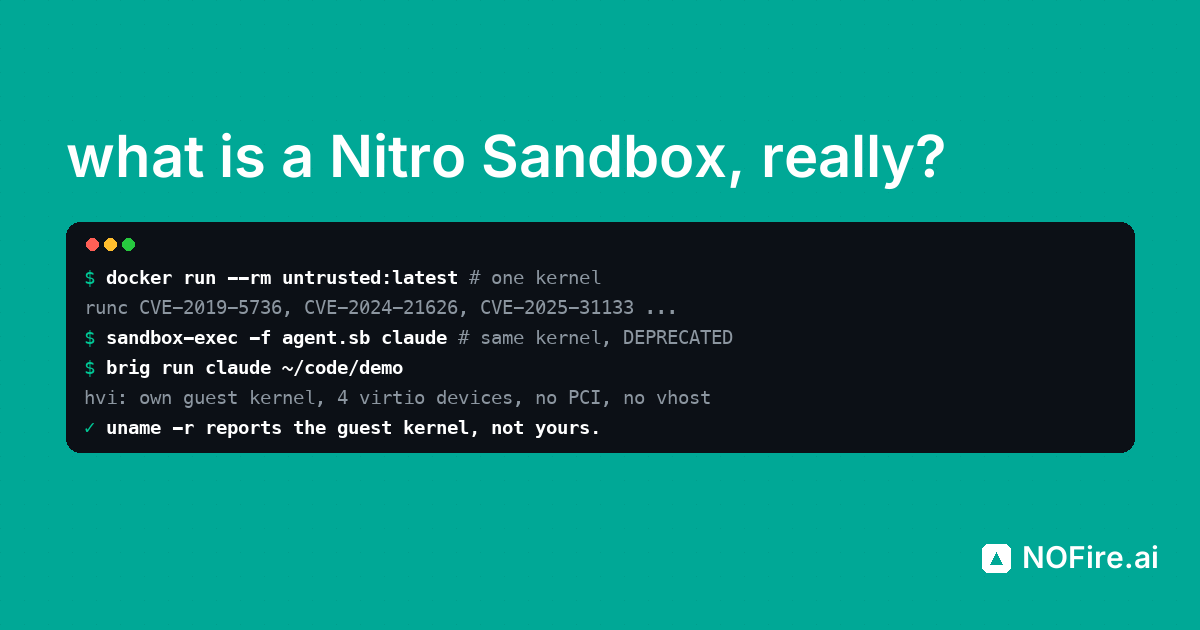
What is an AWS Nitro Sandbox, really?
AWS Nitro Sandboxes give EKS pods, ECS tasks and EC2 workloads hardware-isolated VMs managed by Firecracker without KVM. We examine the architecture, the container and hypervisor escape record, and the reasons Brig uses hvi, a small VMM for macOS and Linux.
Agent evals: measuring the noise before comparing agents
In our previous post we replaced a team of agents with one agent loop. It diagnosed 1.5x as many faults without the Kubernetes tools, at 60% less cost. But there is a problem with evaluating agents. Running the same system twice can give very different results, and in our runs the same build, run twice, moved between 0.65x and 1.38x. So how much of the gain was real and how much was noise? That is what we set out to measure.
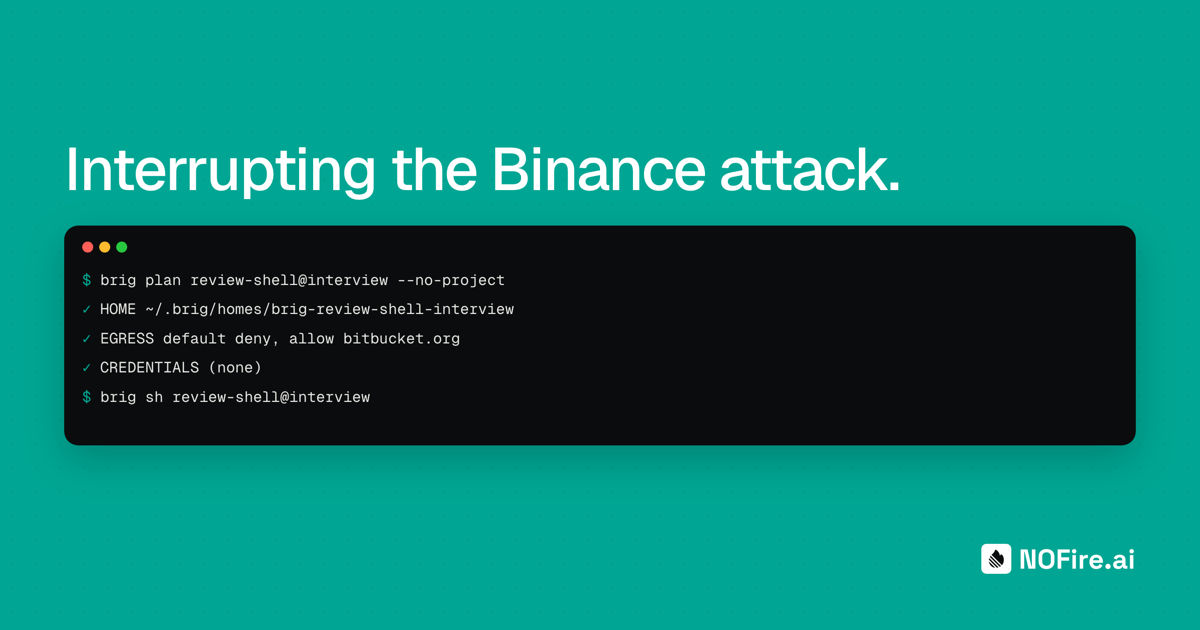
How Brig could have interrupted the Binance attack
Binance's initial incident report names the path a malicious interview repository overwrote on an engineer's laptop. That write is a boundary a microVM sandbox can enforce before anyone knows the code is malicious. This post walks through the Brig v0.5.0 setup that contains it: a disposable guest home, no credentials, an egress allowlist, and a credential broker for the agents that do need an API.
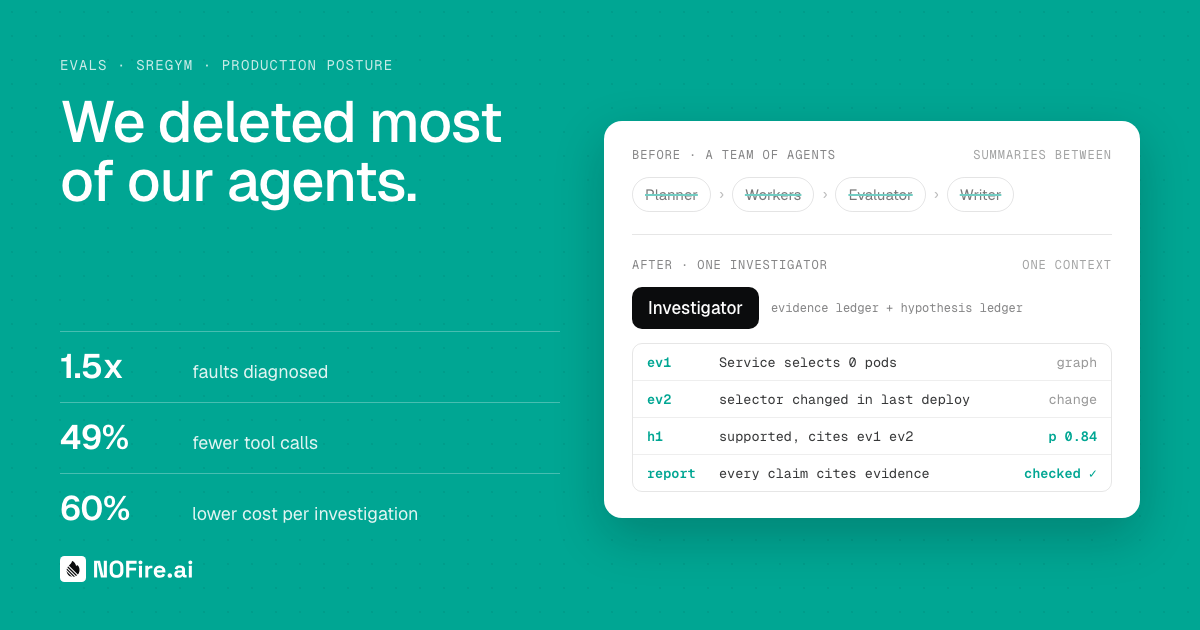
We deleted most of our agents. Our evals told us to.
Earlier this year, we ran NOFire’s root cause investigations on a multi-agent architecture. Daily evals against SREGym and our own test cases showed us what actually improved diagnostic accuracy. A single agent loop delivered the best results: it diagnosed 50% more faults with 49% fewer tool calls, cut the cost per investigation by 60%, and reached a diagnosis 2.5× faster.
Archive
Get production ownership back.
A 30-minute call with a founder. We map your stack to the Context & Control Model, live.